Definition
Search Expressions are a domain-specific language for searching objects (Managed Objects, Reporting collections…) or expressing constraints on them.
A Search Expression combines Property Expressions (e.g. firstName LIKE 'John*') and Functions with Logical Operators (AND, OR, NOT)
securityOrganization <<= 'Finance' AND hasRoleMatching(role IN ('sap_user', 'sap_admin'))
Property Expression
A Property Expression expresses a constraint on a single object property. For Managed Objects, these properties are the Object Attributes.
A Property Expression consists of a Property, an Operator, and one or more Values — for example, firstName = 'John'.
Expression operators
The table below lists all the available operators.
Available operators depend on the use case
|
Operator |
Formula Operator |
Values count |
Meaning for mono-valued Properties |
Meaning for multi-valued Properties |
Allowed value type |
|---|---|---|---|---|---|
|
EQUALS |
= |
1 |
The Property equals the specified value exactly. |
At least one Property Value matches the constraint |
All |
|
EQUALS_LIKE |
~ |
1 |
Same as EQUALS but case-insensitive. |
At least one Property Value matches the constraint |
|
|
NOT_EQUALS |
!= |
1 |
The negation of EQUALS. |
At least one Property Value matches the constraint |
All |
|
NOT_EQUALS_LIKE |
!~ |
1 |
The negation of EQUALS_LIKE, case-insensitive |
At least one Property Value matches the constraint |
|
|
LIKE |
LIKE |
1 |
Searches with wildcards (for example, ma*). Case-insensitive. |
At least one Property Value matches the constraint |
|
|
NOT_LIKE |
NOT LIKE |
1 |
The negation of LIKE. |
At least one Property Value matches the constraint |
|
|
STARTS_WITH |
STARTS WITH |
1 |
The property starts with the specified substring. Case-sensitive. |
At least one Property Value matches the constraint |
|
|
STARTS_WITH_LIKE |
STARTS WITH LIKE |
1 |
Same as STARTS_WITH but case insensitive. |
At least one Property Value matches the constraint |
|
|
ENDS_WITH |
ENDS WITH |
1 |
The property ends with the specified substring. Case-sensitive. |
At least one Property Value matches the constraint |
|
|
ENDS_WITH_LIKE |
ENDS WITH LIKE |
1 |
Same as ENDS_WITH but case-insensitive. |
At least one Property Value matches the constraint |
|
|
CONTAINS |
CONTAINS |
1 |
The property contains the specified substring. Case-sensitive. |
At least one Property Value matches the constraint |
|
|
CONTAINS_LIKE |
CONTAINS LIKE |
1 |
Same as CONTAINS but case-insensitive. |
At least one Property Value matches the constraint |
|
|
BETWEEN |
BETWEEN |
2 |
The value lies between a minimum and a maximum. |
All Property Values match the constraint |
|
|
IN_LAST |
IN LAST |
1 |
The date lies in the past, within the given period. |
All Property Values match the constraint |
|
|
IN_NEXT |
IN NEXT |
1 |
The date lies in the future, within the given period. |
All Property Values match the constraint |
|
|
IN_THE_PAST |
IN THE PAST |
0 |
The date lies in the past, relative to the current date (no period). |
All Property Values match the constraint |
|
|
IN_THE_FUTURE |
IN THE FUTURE |
0 |
The date lies in the future, relative to the current date (no period). |
All Property Values match the constraint |
|
|
IN |
IN |
1 or more |
The Property equals one of the specified values exactly. |
At least one Property Value matches the constraint |
|
|
NOT_IN |
NOT IN |
1 or more |
The negation of IN. |
At least one Property Value matches the constraint |
|
|
GREATER |
> |
1 |
The value is strictly greater than the specified value. |
All Property Values match the constraint |
|
|
GREATER_OR_EQUALS |
>= |
1 |
The value is greater than or equal to the specified value. |
All Property Values match the constraint |
|
|
LESS |
< |
1 |
The value is strictly less than the specified value. |
All Property Values match the constraint |
|
|
LESS_OR_EQUALS |
<= |
1 |
The value is less than or equal to the specified value. |
All Property Values match the constraint |
|
|
BELOW |
<< |
1 |
Searches for children strictly below an Organization (the Organization is excluded). |
At least one Property Value matches the constraint |
|
|
BELOW_OR_EQUALS |
<<= |
1 |
Searches for children below an Organization (the Organization is included). |
At least one Property Value matches the constraint |
|
|
JUST_BELOW |
<<! |
1 |
Searches for direct children of an Organization. |
At least one Property Value matches the constraint |
|
|
ABOVE |
>> |
1 |
Searches for ancestors strictly above an Organization (the Organization is excluded). |
At least one Property Value matches the constraint |
|
|
ABOVE_OR_EQUALS |
>>= |
1 |
Searches for ancestors above an Organization (the Organization is included). |
At least one Property Value matches the constraint |
|
|
JUST_ABOVE |
>>! |
1 |
Searches for objects directly above an Organization (belonging to the parent of the given Organization). |
At least one Property Value matches the constraint |
|
|
IS_NULL |
IS NULL |
0 |
The attribute is blank or empty. |
Not applicable |
All |
|
IS_NOT_NULL |
IS NOT NULL |
0 |
The negation of IS_NULL. |
Not applicable |
All |
Dotted Property Paths
You can express constraints on referenced objects with dotted property paths manager.firstName
For example, for Manage Objects, manager.firstName = 'John' matches all the identities whose manager’s first name is John.
Logical Operators
Use the logical operators AND, OR and NOT to combine Search Expressions, including other logical expressions.
For example: (firstName = 'John' OR firstName = 'Jane') AND lastName = 'Doe'
The Empty Expression
The Empty Expression () is a special Expression matching everything. Its negation NOT () matches nothing.
Search Expression Functions
Search Expression Functions accept one or more Search Expressions as arguments. They are built-in tools for scenarios that a simple Search Expression cannot express:
-
Search identities that have at least one Role Assignment matching a criterion:
hasRoleMatching(role = 'someRole' AND status = 'ASSIGNED') -
Search identities that have a Security Organization matching a criterion:
hasSecurityOrganizationMatching(id BELOW_OR_EQUALS 'europe' AND NOT (id BELOW_OR_EQUALS 'france')) -
Search identities that violate an SoD rule, or Role Assignments involved in an SoD violation:
hasSodViolationMatching(rule = 'someSodRule') -
Search objects that have at least one risk facet row matching a dependency:
hasRiskFacetMatching(dependencies EQUALS objectKind:objectId:Attribute) -
Role Request engine: find assignable Roles based on Role Request Policies.
-
Object Recertification metadata: find the recertifications of an object:
hasRecertificationMetadataMatching(recertifiedAt IN LAST 'P3M') -
Etc.
Usage
UI
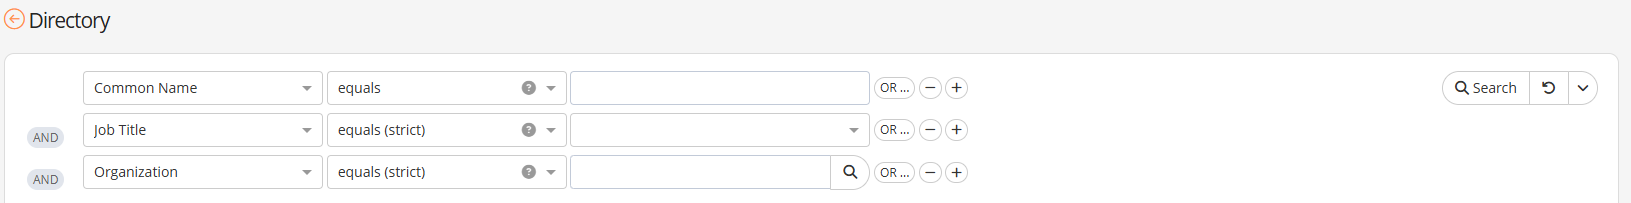
In the user portal, Search Expressions are one of the two ways to search objects, alongside full-text search.
You can enter them graphically for simple expressions, or with a text DSL for complex cases:
Text DSL
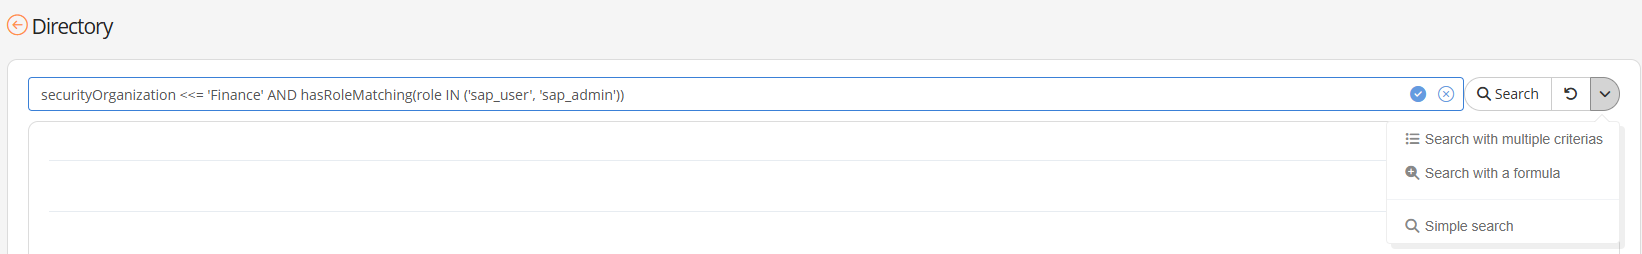
Depending on the configuration, you can enter Search Expressions as plain text:
securityOrganization <<= 'Finance' AND hasRoleMatching(role IN ('sap_user', 'sap_admin'))
Property Expressions
Write Property Expressions as <property name> <operator> <value>:
firstName = 'John'
Syntax rules:
-
The property name can be a single property (
firstName) or a dotted property path (manager.securityOrganization.type). -
Quote property names with double quotes (
") if they don’t start with a Latin letter or an underscore, or if they contain characters other than Latin letters and numbers, for example,"some \"weird\" property". -
Operators are the Formula Operators listed in the table above.
-
Use parentheses for the
INandNOT INoperators, for example,firstName IN ('John', 'Jane'). -
Use
ANDas the separator for theBETWEENoperator:enabledFrom BETWEEN '2022-01-01T00:00:00Z' AND '2023-01-01T00:00:00Z'. -
Quote string values with single quotes (
'), for example,'John \'Johnny\' Doe'. -
Write Date and Date & Time values as ISO 8601 strings, for example, '
2022-11-04' or '2022-11-04T07:30:43Z'. -
Write numbers with the dot (
.) as the decimal separator, for example,-42or+43.756.
Operator Expressions
You can combine arbitrary Search Expressions with the AND, OR, and NOT operators, and with parentheses:
(securityOrganization <<= 'Finance' OR securityOrganization <<= 'Sales') AND hasRoleMatching(role IN ('sap_user', 'sap_admin'))
Functions
Global rules
Write Function Expressions as <function name>(<argument1>, <argument2>,...):
Syntax rules:
-
Function names follow the same quoting rules as Property names
-
Function arguments are always Search Expressions, separated by commas (
,)
hasRoleMatching
The hasRoleMatching function searches identities that have at least one Role Assignment matching a criterion.
The arguments are the RoleAssignment attributes: role, identity, source, parentAssignment, …
hasRoleMatching(role = 'someRole' AND status = 'ASSIGNED')
You can also search identities that have one of several specific roles:
hasRoleMatching(role IN ('sap_user', 'sap_admin'))
hasSodViolationMatching
The hasSodViolationMatching function searches identities that have at least one SoD violation matching the given Search Expression, or Role Assignments involved in at least one such violation.
The arguments are the SodViolation attributes: rule, policy, mode, roleAssignment1, identity, …
hasSodViolationMatching(rule = 'someSodRule')
hasDistinctRoleMatching
The hasDistinctRoleMatching function searches identities that have at least two Role Assignments matching the given Search Expressions.
The arguments are the RoleAssignment attributes: role, identity, source, parentAssignment, …
hasDistinctRoleMatching(role = 'FG3751', status='NORMAL')
hasRiskFacetMatching
The hasRiskFacetMatching function allows to search objects having at least one risk facet row matching the sub-expression.
The arguments are : risk value, dependency ...
hasRiskFacetMatching(dependencies IN objectKind:objectId:Attribute)
XML configuration
Search Expressions appear in the Configuration mostly in Scopes:
-
Features: Feature Scope, Search widgets, Reporting Widgets,…
-
Policies
-
Reference Attributes
-
…
They use the dedicated search namespace.
Property Expressions
<search:Prop op="EQUALS" name="enabled">
    <value>true</value>
</search:Prop>
<search:Prop op="IN" name="firstName">
    <value>John</value>
    <value>Jane</value>
</search:Prop>
In the context of Dynamic Scopes, the value element can contain Groovy code:
<search:Prop op="EQUALS" name="manager">
    <value script="true">OBJECT.id</value>
</search:Prop>
For more information, see Scopes.
Logical Expressions
<search:And>
    <search:Prop op="EQUALS" name="lastName">
        <value>Doe</value>
    </search:Prop>
    <search:Prop op="EQUALS" name="firstName">
        <value>John</value>
    </search:Prop>
</search:And>
<search:Or>
    <search:Prop op="EQUALS" name="firstName">
        <value>Jane</value>
    </search:Prop>
    <search:Prop op="EQUALS" name="firstName">
        <value>John</value>
    </search:Prop>
</search:Or>
<search:Not>
    <search:Prop op="EQUALS" name="manager.firstName">
        <value>John</value>
    </search:Prop>
</search:Not>
Empty Expression
<search:Empty/>
Functions
Groovy Rules
A groovy DSL is available to easily construct Search Expressions:
def emptyExpression = expr {}
def firstNameAndLastNameConstraint = expr {firstName.eq("John") & lastName.eq("Doe")}
def hasO365Role = expr {hasRoleMatching(status.eq(RoleAssignmentStatus.ASSIGNED) & prop("role.application").eq("o365"))}
For more information, see Rules and Actions API.
Special builtin attributes
Some builtin attributes, especially on Identities are not of a simple type (String, Integer, …). This section explains how to search on them
Identity Rights
To match Identities that have a Right Grant, use a Property Expression with the EQUALS or IN operator on the rights Attribute. The Property Expression value must be a String of the form <right name>:<right target>:<right privilege> where you can omit each part:
-
Match all identities that have a specific right, with any target or privilege:
rights = 'app.o365.access' -
Match all identities that have a specific right on a specific target, with any privilege:
rights = 'user.manager:France' -
Match all identities that have a specific right on any target, with a specific privilege:
rights = 'feat.user-card-read::2' -
Match all identities that have a specific right on a specific target with a specific privilege:
rights = 'app.sap.sales:France:1000000'
Identity Roles
You can also match identities by criteria on their Role Assignments, with the hasRoleMatching function. For example:
hasRoleMatching(status = 'ASSIGNED' AND "role.application" = 'o365')
This expression matches all identities that have at least one Role Assignment whose status is ASSIGNED and whose Role matches application = 'o365'.
Role Assignment Dimensions
To match Role Assignments that have certain dimension values, use a Property Expression with the CONTAINS operator on the dimensions property. The value is the JSON serialization of the dimension values to match:
dimensions CONTAINS '{"dim1": "foo", "dim2": ["bar", "baz"]}'
This expression matches all Role Assignments where:
-
dimension
dim1equalsfoo, and -
dimension
dim2contains at leastbarandbaz, in any order.
Read Next